Legacy PLCs and Unsupported Windows: How to Manage Compliance Gaps
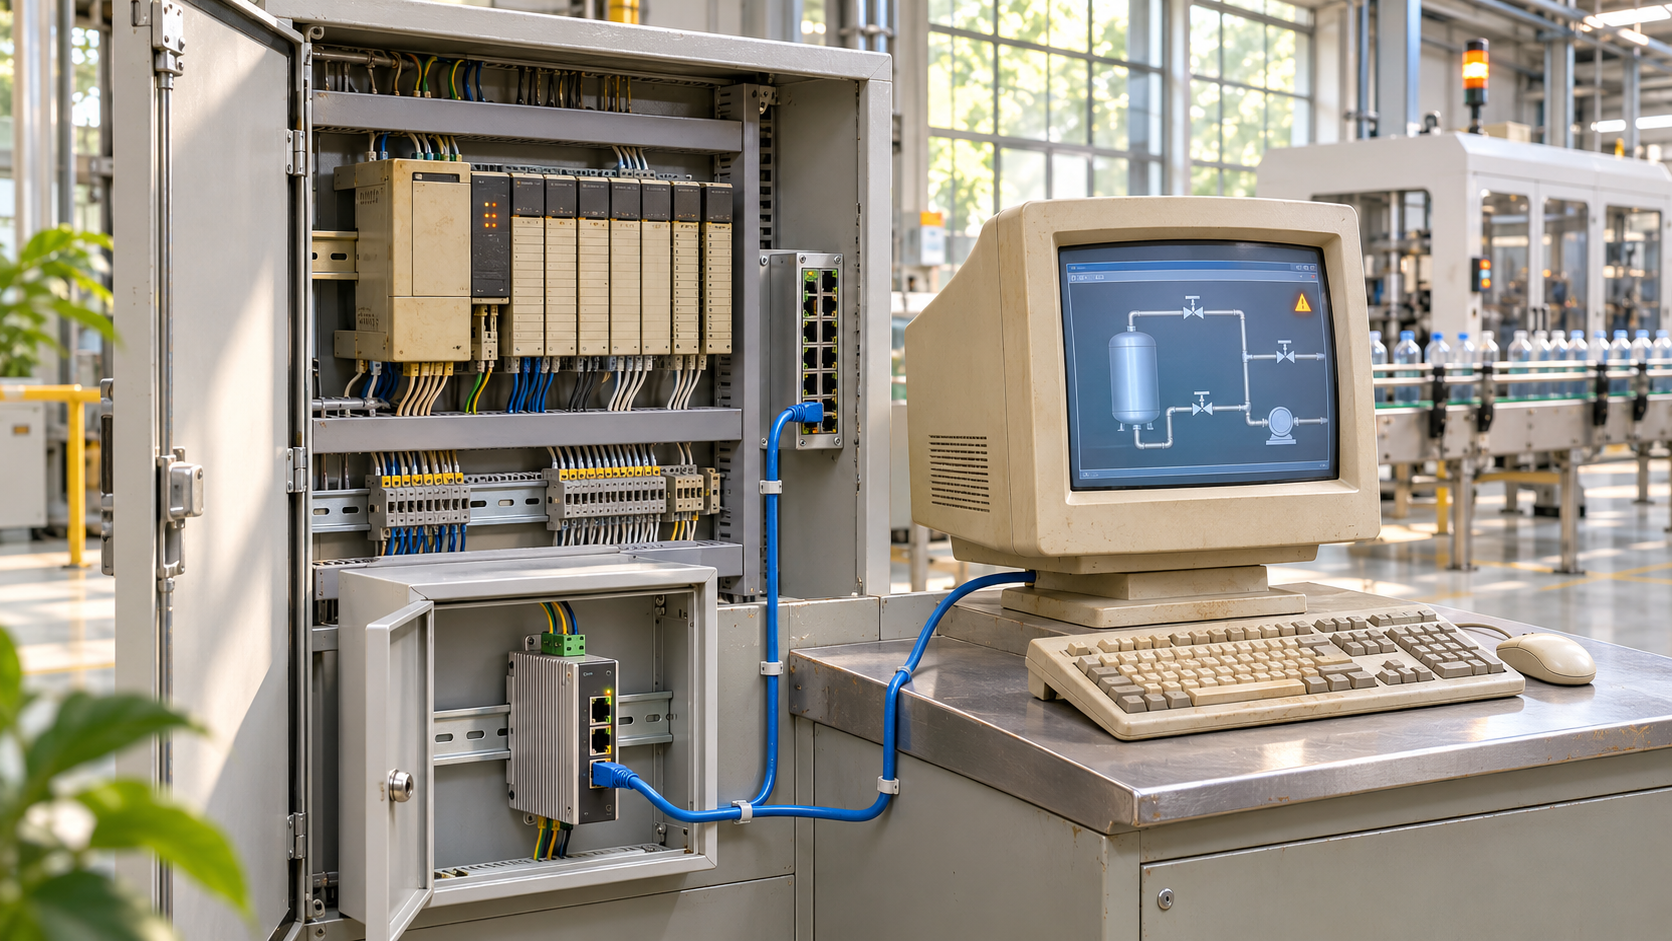
Every industrial site has equipment that cannot be patched. A PLC whose vendor stopped issuing firmware a decade ago. An engineering workstation on a Windows version that stopped receiving updates years back, kept because it is the only machine that runs the software for a controller nobody makes any more. These are not failures of discipline. They are the normal condition of a twenty-year asset base.
The compliance problem is not that the gap exists. Auditors and regulators understand that industrial equipment outlives operating systems. The problem is when the gap is undocumented, which turns a known and managed limitation into an unmanaged one. This article covers how to move legacy equipment from the second category to the first. For equipment you can patch, our guide to OT patch management covers doing it safely.
Four things a defensible position requires
|
Element |
What it means in practice |
|
The limitation, documented |
Which asset, what the constraint is, and why. "No vendor firmware available since 2014" is a finding. "Legacy" is not. |
|
Compensating controls |
What you put in place because you cannot patch. Network position, access restriction, monitoring, physical controls. |
|
Risk acceptance |
A record that someone with authority accepted the residual risk, with a date and a review point. |
|
A replacement plan |
When it goes, roughly what it costs, and what triggers bringing it forward. A plan with no date is a wish. |
All four matter, and the third is the one most often missing. An operator with excellent compensating controls and no record of who accepted the residual risk is in a weaker position with an auditor than one with modest controls and a signed acceptance, because the first cannot demonstrate that the organization knows.
Compensating controls that hold up
When you cannot change the asset, you change everything around it. In rough order of effect:
- Network position. The strongest control available. An unpatchable device that cannot be reached from anywhere it does not need to be reached from is a materially smaller problem. See our segmentation audit guide and the Purdue model.
- Access restriction. Fewer accounts, named individuals, no shared credentials, and no routine use of the legacy workstation for anything else.
- Removable media control. Often the only remaining path into a properly isolated legacy machine, which makes it the path that matters. See removable media security for OT.
- Monitoring. If you cannot prevent, detect. Passive monitoring on the conduit to a legacy zone is proportionate and non-disruptive, covered in building an OT monitoring program.
- Application allowlisting. On an unsupported Windows machine running one known application, allowlisting is more effective than antivirus and often still supported when patching is not.
- Physical control. A locked cabinet and a disabled USB port are real controls, and they are the ones a legacy environment can usually still implement.
|
The honest framing for an auditor Do not present legacy equipment as a problem being solved. Present it as a risk being managed, with the controls named, the acceptance recorded and the replacement scheduled. Auditors see unpatchable equipment at every industrial site they visit. What distinguishes a good position from a poor one is whether the organization can show it knows which assets they are, what it has done instead, and who decided that was enough. |
The Windows problem specifically
Unsupported Windows in OT is usually a software dependency rather than a hardware one. The machine is kept because a vendor tool, a license dongle or a driver will not run on anything newer. That distinction matters because it changes the remedy: the question is not "can we upgrade this PC" but "can this application run anywhere else".
Three routes are worth assessing before accepting the machine as permanent. Virtualizing the legacy environment moves the dependency off ageing hardware and makes backup and recovery straightforward, though it does not fix the operating system exposure. Checking whether the vendor has released a current version of the tool is often skipped, and sometimes answers the question outright. And where the machine exists solely to configure one controller, the honest cost comparison is against replacing the controller, which may be cheaper than carrying the exposure for another decade.
Building a replacement plan you can defend
Rank legacy assets by consequence rather than age. A twenty-year-old controller running a non-critical utility is a lower priority than a ten-year-old one in a safety-related function, regardless of which looks worse on an inventory. Then attach three things to each: an indicative replacement window, a rough cost, and a trigger that would bring it forward, such as a vendor announcement, a failure, or a change in the regulatory position.
Tie the plan to capital cycles rather than treating it as a security project. Legacy equipment is most cheaply replaced during a planned upgrade or turnaround that was happening anyway, and a security case attached to an existing capital item is funded far more often than a standalone one.
Why Choose Arista Cyber
We assess legacy estates on running plants and we are candid about which controls are proportionate, because recommending a replacement program nobody will fund helps nobody. Our consultants hold functional safety credentials alongside OT security certification, so where legacy equipment sits in a protective function we assess the safety consequence of leaving it and of changing it. See our OT risk assessments and our case studies.
Next Steps
List the equipment you cannot patch, rank it by consequence rather than age, and check whether a risk acceptance record exists for each. In most plants the list is shorter than feared and the missing acceptance records are the quickest gap to close.
Common Questions
Is running unsupported Windows in OT a compliance violation?
Not inherently. Most frameworks accept that industrial equipment outlives operating systems. What they do not accept is an undocumented gap. The position becomes defensible when the limitation is recorded, compensating controls are in place, residual risk is formally accepted and a replacement plan exists.
What is the best compensating control for an unpatchable device?
Network position. Restricting what can reach the device, and what it can reach, reduces the exposure more than anything else available once patching is off the table.
Do we need a formal risk acceptance record?
Yes, and it is the element most often missing. Strong technical controls without a record of who accepted the residual risk leave you unable to demonstrate that the organization knows about the gap.
How should we prioritize legacy replacement?
By consequence, not age. A newer controller in a safety-related function outranks an older one on a non-critical utility. Attach an indicative window, a rough cost and a trigger that would accelerate it.
Is antivirus useful on an unsupported Windows machine?
Less than application allowlisting. On a machine running one known application, allowlisting is both more effective and more likely to still be supported than signature-based antivirus on an operating system that no longer receives updates.
|
Carrying equipment you cannot patch? Arista Cyber assesses legacy OT estates and builds the defensible position: documented limitations, proportionate compensating controls, risk acceptance records and a replacement plan tied to your capital cycle. |
Facing tougher cyber security challenges?
Talk to Arista Cyber about your OT security posture.
Request a consultation